A Firewall Is Only as Good as the Way It Is Deployed

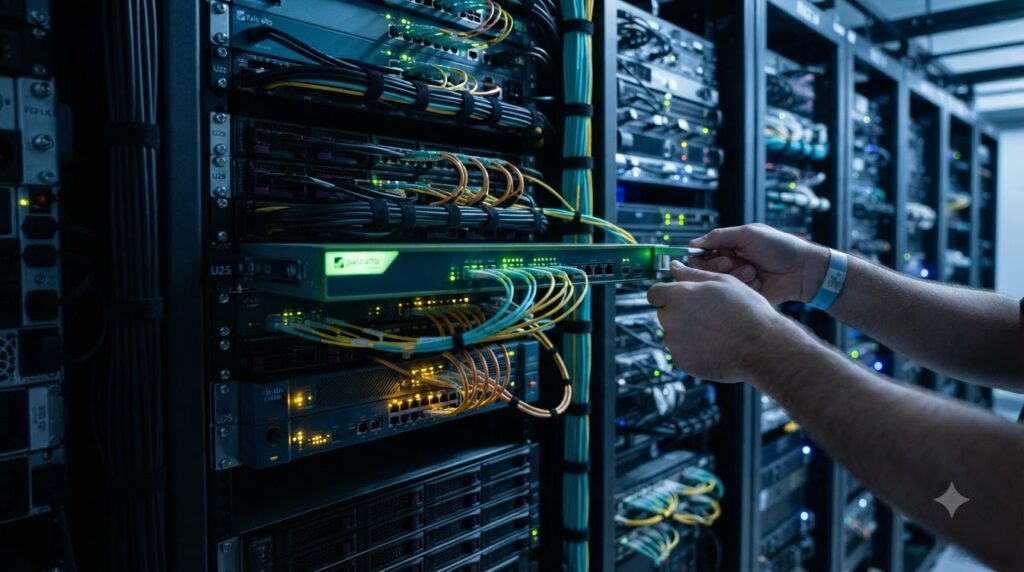
A next generation firewall can inspect traffic, control applications, and stop threats, but only if it is designed, configured, and tuned for your environment. Datacipher deploys leading firewall platforms and gets the policy, segmentation, and rules right, so the capability you paid for is the capability you actually get.

Business Challenges

The Firewall Was Installed, Then Left Alone
A powerful platform is only as effective as its configuration, and many are running on rules set once at install and never revisited.
Years of additions leave a rule base so large and contradictory that no one is sure what is still needed or what it is actually allowing through.
Application control, threat prevention, and inspection are licensed but never fully turned on, so the investment sits idle.
With little segmentation inside the perimeter, anything that does get through can move freely across the network.
A growing share of traffic is encrypted, and where it is not being inspected, threats travel inside it unseen.

Our Solution

Datacipher designs and deploys next generation firewall solutions built on leading OEM platforms, configured around your network, your applications, and the risks you actually face. We do not just install the appliance. We build the policy, define the segmentation, tune the rules, and turn on the protective features that too often go unused.

We begin by understanding how traffic moves through your environment and what needs protecting, then translate that into a firewall policy that is effective without getting in the way of the business. Where you are replacing older firewalls, we plan the migration so protection is never dropped during the change.

Key Features

Policy Built Around Your Environment

Firewall and application control policy designed for how your business actually operates, rather than a generic default rule set.

Application and User Aware Control

Rules based on the specific applications and users involved, not just ports and addresses, so access reflects what people actually need.

Threat Prevention Fully Enabled

Intrusion prevention, malware inspection, and threat feeds configured and switched on, so the platform's protective capabilities are actually in use.

Internal Segmentation

Firewall policy used to separate the network into zones, so a threat that reaches one area cannot move freely into the rest.

Encrypted Traffic Inspection

Inspection of encrypted traffic designed in where appropriate, so threats cannot use encryption as a blind spot, with privacy and performance accounted for.

Planned Migration From Legacy Firewalls

Where older firewalls are being replaced, the cutover is staged and the rule base is reviewed and cleaned as it moves, so protection is never dropped during the change.

Business Benefits

1

The Protection You Actually Paid For

Features that were licensed but never enabled are put to work, so the platform delivers its full value instead of a fraction of it.

2

Threats Stopped, Not Just Slowed

A properly tuned policy with prevention enabled blocks far more than a default configuration ever will.

3

Damage Contained When Something Gets In

Internal segmentation limits how far an attacker or an infection can spread beyond the point of entry.

4

Fewer Blind Spots

Inspecting encrypted traffic closes one of the most common gaps attackers rely on to move unseen.

5

A Rule Base You Can Trust Again

Cleaning up and structuring the policy means the firewall does what you think it does, which makes audits and changes far easier.

Solution Architecture

The firewall solution is designed to integrate with your existing network and security tools, and where it replaces older firewalls, the migration is planned so protection remains continuous throughout the change.

OEM Partners

Built on leading next generation firewall platforms from Palo Alto Networks, Juniper Networks, and other OEMs, with the platform selected to fit your environment, your existing estate, and your security requirements.

Image gallery marquee

Proven Customer
Outcomes

Delivering measurable business results through enterprise networking, cybersecurity, and cloud solutions that improve performance, resilience, and operational efficiency.
Case Study

From 20 Hours of Downtime to Under 1 Hour

DDoS attacks were knocking RailTel offline for nearly 20 hours a month. For one of India’s largest telecom providers, that couldn’t continue. Datacipher deployed Corero’s hybrid DDoS protection, phased in with zero disruption. Downtime fell to under an hour, and attacks now get blocked in real time.

Case Study

50% More Capacity, 70% Fewer Complaints

Rising user demand had pushed QTL’s network into constant congestion, dragging down service quality and pushing customer complaints higher every month. Datacipher upgraded the network with Juniper MX Series routers, rolled out in off-peak hours to avoid disruption. It helped lift overall capacity by 50%, and and cutting performance complaints by 70%.

Case Study

80% Fewer Wi-Fi Dropouts

Mahindra & Mahindra’s ageing Wi-Fi couldn’t keep up with a growing number of devices. Staff hit constant dropouts, and productivity slipped. Datacipher moved them to Juniper Mist, an AI-driven wireless network, phased in with minimal downtime. Connectivity issues fell 80%, and speeds rose 30%.

Case Study

A Data Center Move With Zero Downtime

With its lease expiring and its infrastructure past its prime, Technicolor had just six months to move its entire data center without disrupting a global media operation. Datacipher planned and ran the migration in carefully coordinated phases, hitting the deadline with zero unplanned downtime and moving Technicolor onto faster, more reliable infrastructure.

Case Study

60% Fewer Incidents, 35% Faster

BESCOM’s branch offices were running on outdated firewalls. They couldn’t handle modern threats or rising traffic, so security gaps and slowdowns crept in. Datacipher replaced them with Juniper SRX1500 firewalls, migrating every policy in phases. Security incidents fell 60%, and performance improved 35% across sites.

Case Study

20% More Revenue From New Services

Kerala Vision Broadband wanted to launch new, competitive services but was boxed in by its existing network. Datacipher upgraded the infrastructure with Juniper MX Series routers, adding support for advanced offerings like MPLS-based VPNs. The ISP piloted the services, rolled them out, and lifted revenue 20% in six months.

Why Datacipher

650+ Projects, Proven at Scale

A track record of enterprise engagements delivered across industries.

We Deploy It, We Do Not Just Sell It

Our value is in designing the policy, tuning the rules, and enabling the protection, which is the work that decides whether a firewall actually defends you.

Vendor Agnostic by Design

Deep expertise across leading firewall platforms means we recommend and configure what fits your environment, not what suits a single vendor.

Support That Doesn't End at Go-Live

Continued monitoring and support through our dedicated Security Operations Center.

FAQs

We already have next generation firewalls. Do we need new ones?
Often not. A great deal of value comes from properly configuring, tuning, and enabling the features on the firewalls you already own, and we frequently start there rather than with replacement.
Not when it is sized and designed correctly. We plan inspection and throughput around your actual traffic, so protection is enabled without creating a bottleneck.
The migration is planned in stages so that protection is never dropped, with rules reviewed and cleaned up as they are moved rather than copied across as they are.
Yes. Encrypted inspection is designed selectively, with sensitive and regulated traffic handled appropriately, so you gain visibility without unwanted side effects.
We design and deploy the full solution, including policy, segmentation, and threat prevention. The platform is the OEM’s. Making it work for your environment is what we do.

Latest from Datacipher

Ready to get the full protection your firewall is capable of?