Zero Trust Is a Model. Making It Work Is the Hard Part.

Everyone agrees with the principle: trust nothing by default, verify every request. The difficulty is turning it into working controls across identity, devices, and applications, using the right products for your environment. That integration is what Datacipher does, bringing proven zero trust platforms together into an architecture that actually holds.

Business Challenges

Being Inside the Network Means Being Trusted
Once someone is past the perimeter, traditional networks tend to trust them by default, so a single breach can turn into free movement across everything.
When access is broad, a single stolen credential or infected device can touch far more of the business than it ever should.
Most teams accept zero trust in theory but stall on execution, because it spans identity, devices, network, and data rather than sitting in one place.
The market offers dozens of zero trust products across different layers, and buying them is easy, but making them work together as one coherent model is not.
Users, devices, and applications now sit inside and outside the network at once, and a perimeter based model was never built for that.

Our Solution

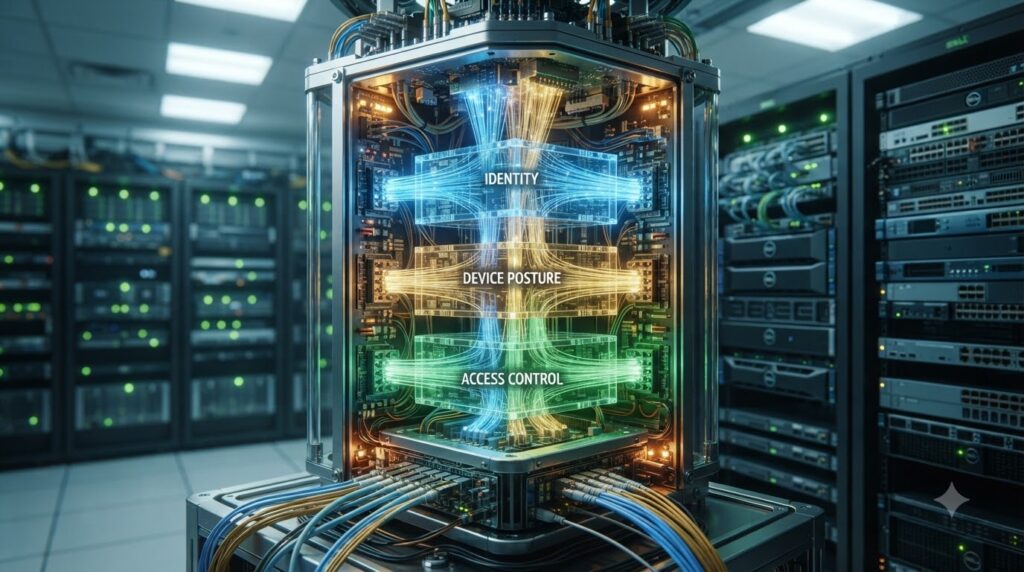
Zero trust is a well-established security model, and the market has strong products to deliver each part of it. The real challenge is choosing the right ones for your environment and integrating them so identity, device posture, access control, and segmentation work together as a single architecture rather than a pile of separate tools. That integration is where Datacipher works.

We start by understanding your users, your applications, and where your most sensitive systems and data sit. From there we help you select the right platforms across each layer of zero trust, deploy them, and connect them into your existing identity, endpoint, and network systems. We implement it in practical stages, so each step delivers a real security gain without disrupting how people work, and you are never left with technology you cannot operate.

Key Features

The Right Platforms for Each Layer

We help you select identity, access, and segmentation products that fit your environment, rather than forcing everything onto one vendor or one tool.

Identity as the Foundation

We deploy and integrate strong identity verification, so access decisions rest on who the user is, not on where they are connecting from.

Device Posture Checks

We implement controls that assess the security state of a device before access is granted, so a compromised or outdated device does not walk straight in.

Least Privilege and Segmentation

We configure access and microsegmentation across the chosen platforms, so users reach only what they need and a threat cannot move freely.

Everything Integrated as One Model

We connect the separate products into a coherent architecture with consistent policy, which is the work that turns zero trust from idea into reality.

Business Benefits

1

Breaches That Stay Small

When nothing is trusted by default and access is tightly scoped, an attacker who gets in finds very little they can reach or move toward.

2

Far Less Damage From Stolen Credentials

Least privilege and continuous verification mean a single compromised account is no longer a key to the whole business.

3

Products That Work Together, Not Against Each Other

Integrating the right platforms into one model removes the gaps and conflicts that appear when tools are bought separately and never connected.

4

A Path You Can Actually Follow

Delivered in stages, zero trust becomes a set of achievable steps rather than a programme too big to begin.

5

Technology You Can Operate

Because we integrate into your existing systems and hand over what we build, you are left with an architecture your team can run, not a black box.

Solution Architecture

Zero trust is implemented across your existing identity, endpoint, and network systems using selected OEM platforms, integrated into one architecture and rolled out in stages so each control strengthens the model without disrupting day to day work.

OEM Partners

Built using leading zero trust, identity, and access platforms from OEMs including Palo Alto Networks and Microsoft, selected for each layer of the architecture and integrated to fit your existing identity, endpoint, and network environment.

Image gallery marquee

Proven Customer
Outcomes

Delivering measurable business results through enterprise networking, cybersecurity, and cloud solutions that improve performance, resilience, and operational efficiency.
Case Study

From 20 Hours of Downtime to Under 1 Hour

DDoS attacks were knocking RailTel offline for nearly 20 hours a month. For one of India’s largest telecom providers, that couldn’t continue. Datacipher deployed Corero’s hybrid DDoS protection, phased in with zero disruption. Downtime fell to under an hour, and attacks now get blocked in real time.

Case Study

50% More Capacity, 70% Fewer Complaints

Rising user demand had pushed QTL’s network into constant congestion, dragging down service quality and pushing customer complaints higher every month. Datacipher upgraded the network with Juniper MX Series routers, rolled out in off-peak hours to avoid disruption. It helped lift overall capacity by 50%, and and cutting performance complaints by 70%.

Case Study

80% Fewer Wi-Fi Dropouts

Mahindra & Mahindra’s ageing Wi-Fi couldn’t keep up with a growing number of devices. Staff hit constant dropouts, and productivity slipped. Datacipher moved them to Juniper Mist, an AI-driven wireless network, phased in with minimal downtime. Connectivity issues fell 80%, and speeds rose 30%.

Case Study

A Data Center Move With Zero Downtime

With its lease expiring and its infrastructure past its prime, Technicolor had just six months to move its entire data center without disrupting a global media operation. Datacipher planned and ran the migration in carefully coordinated phases, hitting the deadline with zero unplanned downtime and moving Technicolor onto faster, more reliable infrastructure.

Case Study

60% Fewer Incidents, 35% Faster

BESCOM’s branch offices were running on outdated firewalls. They couldn’t handle modern threats or rising traffic, so security gaps and slowdowns crept in. Datacipher replaced them with Juniper SRX1500 firewalls, migrating every policy in phases. Security incidents fell 60%, and performance improved 35% across sites.

Case Study

20% More Revenue From New Services

Kerala Vision Broadband wanted to launch new, competitive services but was boxed in by its existing network. Datacipher upgraded the infrastructure with Juniper MX Series routers, adding support for advanced offerings like MPLS-based VPNs. The ISP piloted the services, rolled them out, and lifted revenue 20% in six months.

Why Datacipher

650+ Projects, Proven at Scale

A track record of enterprise engagements delivered across industries.

Integration Is the Product

Anyone can buy zero trust tools. Our value is choosing the right ones for your environment and making them work together as one architecture, which is the part that actually delivers the model.

Vendor Agnostic Across Every Layer

Because we work across identity, access, and segmentation platforms rather than one, we build the architecture around your needs instead of a single vendor's stack.

Support That Doesn't End at Go-Live

Continued monitoring and support through our dedicated Security Operations Center.

FAQs

Is zero trust a product Datacipher sells?
No. Zero trust is a security model, and the products that deliver it are built by OEMs. What we provide is the expertise to select the right platforms for your environment and integrate them into a working architecture.
Yes. Very often the tools are already in place but not integrated or configured to work as one model. Bringing what you have into a coherent architecture is a large part of what we do.
Usually with identity and access, since strong verification and least privilege deliver a large share of the benefit early. We then extend to device posture and segmentation in stages.
Generally no. Zero trust is built across the identity, endpoint, and network systems you already have, adding or integrating platforms where there are gaps rather than starting over.

It is an ongoing program rather than a one time project, but it delivers value at each stage. We plan the sequence so early steps produce real security gains while later ones build on them.

Latest from Datacipher

Ready to turn zero trust from a principle into a working architecture?